Google Earth Has a Secret Flight Simulator Hiding in Plain Sight — Here’s How to Fly It

Most people open Google Earth for two reasons: checking what their childhood home looks like from space, or scoping out a vacation rental before booking it. But tucked right inside Google Earth is an entire 3D flight simulator waiting to be switched on.

No expensive flight sticks required. No paid expansions. Just a quick setting or a secret three-key combo that drops you right into the cockpit of an airplane buzzing over real 3D terrain anywhere on the planet.

Whether you’re stuck on a boring conference call or just want to see what your daily commute looks like at Mach 1, here’s how to fire it up—both right in your web browser and in the classic desktop version.


Option 1: Play Right in Your Web Browser (Zero Install)

If you’re on a locked-down work laptop or a Chromebook where you can’t install desktop software, don’t worry. You can run the flight simulator directly inside Chrome, Edge, or Firefox without downloading a single file.

Here is the browser path:

  1. Head to Google Earth: Open your desktop browser and go to earth.google.com.
  2. Initialize the 3D globe: Click the Explore Earth button on the landing page to load the full 3D WebGL engine.
  3. Pick your scenery: Use the search box or spin the globe to center on the area you want to fly over (the Swiss Alps, downtown Tokyo, or the Grand Canyon are awesome starting spots).
  4. Open the Tools menu: In the top navigation bar, click on Tools.
  5. Launch the sim: Select Flight simulator from the dropdown menu.

That’s it. Your browser switches into 3D flight mode immediately. You can throttle up using Page Up, pitch and bank with your arrow keys or mouse, and cruise over real satellite photogrammetry in full screen.


Option 2: The Classic Full-Fidelity Desktop App (Google Earth Pro)

The browser version is great for quick fun. But if you want the original, full-featured flight simulator—with realistic head-up telemetry, dual aircraft selection, flap controls, and actual airport runway takeoffs—you want Google Earth Pro for Desktop.

It’s completely free to download from Google for Windows, macOS, and Linux.

The Secret Easter Egg Keystroke

Back in 2007, a couple of clever Google engineers quietly slipped the flight sim into Google Earth 4.2 as an unannounced Easter egg. Tech forums caught wind of the secret keystroke, and it became so wildly popular that Google kept it permanently.

Once you open Google Earth Pro on your desktop, launch it with:

  • Windows & Linux: Press Ctrl + Alt + A
  • Mac: Press Command + Option + A
  • Or via the menu: Click Tools > Enter Flight Simulator…

A dialog window will pop up asking you to pick your wings and your departure runway.

Pick Your Aircraft

  • F-16 Fighting Falcon: Raw speed, twin-engine afterburners, and knife-edge agility. It climbs like a rocket, but one heavy twitch of the mouse will put you into the side of a skyscraper.
  • SR22 (Cirrus SR22): A four-seat, single-engine propeller plane. Slower, much more forgiving, and ideal if you actually want to look out the window at the scenery. Start here.

Pick Your Starting Runway

You can line up on the runway at dozens of international airports—like Los Angeles (LAX), Zurich, Kathmandu (Lukla for an extreme challenge), or Sydney. Or choose Current view to spawn mid-air right above wherever you were looking before opening the menu.


Flight Controls: How Not to Crash in 15 Seconds

Google Earth supports USB joysticks if you have one plugged into your rig. But most of us will be flying with mouse and keyboard.

The moment flight mode starts, click once right in the middle of the screen. Your mouse cursor turns into a small + crosshair. That crosshair acts as your flight stick—push forward to dive, pull back to climb, and nudge left or right to bank.

ActionKeyboard Command
Throttle UpPage Up
Throttle DownPage Down
Pitch Down / Up (Elevators)Mouse push forward / pull back (or Up / Down Arrows)
Bank Left / Right (Ailerons)Mouse move left / right (or Left / Right Arrows)
Rudder Left / RightInsert / Enter (numeric keypad), or Shift + Left / Right Arrow
Extend FlapsF
Retract FlapsShift + F
Landing Gear ToggleG
Wheel Brakes, (left brake) and . (right brake)
Pause / UnpauseSpacebar
Exit Flight SimEscape

Reading the Head-Up Display (HUD)

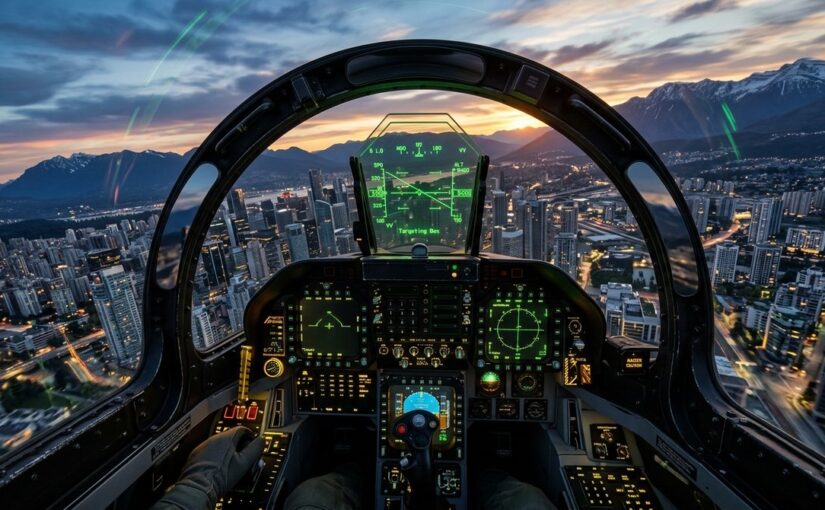
In the desktop version, you’ll see a green HUD overlay drawn right across the horizon:

  • Speed (Knots): The number in the top-left corner. If your speed drops below 60 knots in the SR22, you’ll stall.
  • Heading: The degree numbers at the top center showing your compass direction.
  • Pitch & Bank Ladder: The parallel horizontal lines in the middle showing your artificial horizon. Keep the crosshair centered on the horizon line for level flight.
  • Altitude (Feet): The numbers in the top-right corner showing your height above sea level.
  • Throttle Bar: The vertical gauge on the bottom left. 100% means full power.
  • Flaps & Gear Indicators: Small readout indicators on the bottom right telling you whether your landing gear is down or your flaps are extended.

Four Survival Tips for Rookie Pilots

1. Take off smoothly: Tap Page Up until your throttle reaches 100%. Keep the plane centered on the tarmac. Once the SR22 reaches about 75 knots (or the F-16 hits 160+ knots), pull back gently on the mouse. Yanking it too hard guarantees an instant stall.

2. Retract your gear: Hit G as soon as you clear the runway. Leaving your wheels down creates heavy aerodynamic drag and prevents you from gaining altitude.

3. Use micro-movements: Mouse steering is sensitive. Keep the + crosshair inside the center box. Millimeter movements are all it takes to bank cleanly.

4. Don’t panic—hit Spacebar: If you find yourself in a terrifying inverted tailspin over downtown Manhattan, hit Spacebar to freeze the simulation. Center your mouse cursor, breathe, and press Spacebar again to level out.

It won’t replace a multi-gigabyte modern simulator rig, but having an instant 3D airplane engine tied directly to planet-scale satellite data right on your machine is still one of the coolest hidden features on the internet. Go take a flight.
Why the Top Link on Google Is Now the Most Dangerous Click on the Internet

Here is a common scenario: You just set up a brand new computer or need to play a video file. You open your browser, type “VLC Media Player” or “7-Zip” into Google, and click the very first link at the top of the search results.

The website looks completely legit. It has the official logo, screenshots, and a big blue “Download Now” button. You download the installer, double-click it, and… maybe an error pops up, or maybe the software actually installs.

What you don’t realize is that in the background, a silent piece of malware just vacuumed up every saved password in your browser, grabbed your active login cookies (bypassing Two-Factor Authentication), copied your autofill credit cards, and sent them to a server overseas.

Welcome to Search Engine Malvertising—one of the fastest-growing cyber threats that the FBI recently had to issue a nationwide warning about.


How Criminals Buy the #1 Spot on Google

For decades, we’ve been conditioned to believe that the top search result on Google is the most authoritative and trustworthy source. Cybercriminals know this, and they exploit that trust mercilessly.

Instead of trying to hack Google or spend years on SEO, hackers simply purchase Google Search Ads. Because paid ads appear at the very top of the page—above all organic search results—their malicious links get clicked first.

Popular targets frequently impersonated in Google Ads include: VLC Media Player, OBS Studio, Notepad++, AnyDesk, 7-Zip, WinRAR, Canva, GIMP, and various cryptocurrency wallets.

Why Doesn’t Google Block These Ads Instantly?

You might wonder: “Doesn’t Google review every ad before it goes live?”

They do, but attackers use a clever evasion technique known as cloaking:

  • When Google’s automated verification bot scans the ad link, the server detects the bot and serves a completely harmless, squeaky-clean website (like a generic software blog or travel guide). The ad gets approved.
  • When a real human user clicks the ad from Google Search, the server detects a genuine visitor and redirects them to an identical clone of the real software’s website hosted on a lookalike domain (for example, vlc-download-app.com instead of videolan.org).

The Dangerous Payload: “Infostealers”

These fake installers typically bundle notorious infostealers like Lumma, RedLine, or Vidar. These programs don’t lock your screen demanding ransom—they operate in total stealth:

  • They harvest all usernames and passwords saved inside Chrome, Edge, Firefox, and Brave.
  • They steal your session tokens (cookies). This means an attacker can paste your cookies into their browser and log directly into your Amazon, Google, or bank account—without ever needing to enter your password or pass 2FA.
  • They scan your clipboard for crypto wallet addresses and replace them with the attacker’s wallet.

How to Protect Yourself: 4 Simple Rules

1. Train Your Eyes to Skip the “Sponsored” Badge

Whenever you search for software, drivers, or financial tools, pause for a second before clicking. Look at the tiny text right above the link title:

  • If you see “Sponsored” or “Ad”, skip it entirely.
  • Scroll down to the first organic result. The official website will almost always be the top organic result with the clean, recognizable domain name.

2. Install a Content Blocker (It’s a Security Tool, Not Just a Convenience)

Many people view ad blockers as a way to avoid annoying popups or YouTube ads. In today’s threat landscape, a good open-source content blocker like uBlock Origin is a critical security layer.

Content blockers automatically hide search engine sponsored ads and block known malicious redirect domains, effectively defusing the trap before you can ever click it.

3. The IT Pro Secret: Use Windows Package Manager (winget)

Why search sketchy websites at all when Windows has a built-in, verified app repository? If you are on Windows 10 or 11, you can install trusted software in seconds without even opening a browser:

  1. Press Windows Key + X and choose Terminal (or PowerShell).
  2. Type: winget install VideoLAN.VLC or winget install 7zip.7zip and press Enter.

Windows downloads the authentic, hash-verified installer directly from the official source repository. Zero ads, zero fake download buttons, zero malware.

4. What If You Think You Already Ran a Fake Installer?

If you recently downloaded an app and noticed odd behavior (like a command prompt flashing briefly, or the app never actually opening):

  1. Disconnect immediately: Unplug Ethernet or disconnect from Wi-Fi to stop ongoing data exfiltration.
  2. Use a DIFFERENT clean device: Do NOT change passwords from the infected computer. Use your smartphone to log into your primary accounts (Google, Apple, banking, password manager).
  3. Terminate active sessions: In your account security settings, click “Log out of all devices” or “Revoke all sessions” to invalidate any stolen session cookies.
  4. Run an offline scan: Perform a full scan using Windows Defender Offline or a rescue USB drive with Malwarebytes.

The Bottom Line

Google search is still an incredible tool, but search engine ads have become a digital minefield for everyday software downloads. Take an extra two seconds to verify the real domain, install an ad blocker on all family devices, and remember that being at the top of Google doesn’t mean it’s safe.

Why Changing Your Gmail Password Isn’t Enough: The Hidden Delegation Backdoor You Need to Check Right Now

Imagine this chilling scenario: You suspect something is off with your email. You do everything the cybersecurity textbooks tell you to do—you change your password to a 20-character fortress, turn on Two-Factor Authentication (2FA), and hit “Sign out of all other web sessions”.

You breathe a sigh of relief. You think you’re completely safe.

Yet, weeks later, you discover the shocking truth: someone has still been reading your private emails, tracking your bank alerts, and monitoring your personal conversations in real time.

How is this even possible? Did a hacker deploy sophisticated spyware? Did Google have a catastrophic zero-day breach?

The answer is much simpler—and far more unsettling. It’s a legitimate, built-in Gmail feature that operates as a silent backdoor if someone had access to your unlocked screen for just two minutes.


The Culprit: Gmail Account Delegation

Inside Gmail lies a productivity tool called Account Delegation (“Grant access to your account”).

Originally engineered for executives who need an executive assistant to organize their inbox, or teams sharing a common mailbox, delegation allows another Google account to:

  • Read all your incoming and outgoing emails.
  • Send new emails on your behalf.
  • Delete or archive sensitive messages.
  • Access your contacts list.

Here is the dangerous catch:

A delegated user does not log into your account with your password. They log into their OWN Gmail account and switch to your inbox from their profile menu.

Because they access your emails from their own credentials:

  • Changing your password does not remove them.
  • Enabling 2FA does not block them.
  • Clicking “Sign out of all sessions” does not revoke their access.
  • You won’t get suspicious login notifications because nobody is logging into your account.

All it takes is an ex-partner, a jealous coworker, an abusive acquaintance, or someone who borrowed your unlocked laptop for a coffee break to add their email address to your delegation list. Once accepted, they have permanent, invisible visibility into your digital life.


How to Check and Close the Backdoor Right Now

Checking your Gmail for unwanted access takes less than 60 seconds. Grab your computer (this must be done in the desktop web browser, as mobile apps don’t display all advanced settings) and perform these 4 quick audits:

1. Check for Unauthorized Delegates

  1. Open Gmail on your computer.
  2. Click the Settings gear icon in the top-right corner and select “See all settings”.
  3. Click on the “Accounts and Import” (or “Accounts”) tab at the top.
  4. Scroll down to the section titled “Grant access to your account”.
  5. Inspect the list: If you see any email address you didn’t personally add, click “Delete” immediately.

2. Check for Sneaky Forwarding Rules & Hidden Filters

Another classic backdoor tactic is setting up silent forwarding rules or automated filters that instantly copy incoming mail to an outside address or mark security warnings as “Read” and “Archive”.

  • While still in Gmail Settings, click the “Forwarding and POP/IMAP” tab. Verify that no unrecognized address is receiving forwarded copies of your mail.
  • Click on the “Filters and Blocked Addresses” tab. Review every rule listed. Look out for suspicious instructions like “Matches: from(*) Do this: Forward to evil@example.com, Delete it”. If you see anything you didn’t create, delete it.

3. Audit Third-Party App Permissions

Sometimes access isn’t a person—it’s an abandoned browser extension, a forgotten email cleaner app, or a compromised productivity tool that requested full access to your Google mailbox.

  1. Go to your Google Account Connected Apps.
  2. Review apps with “Full Account Access” or access to Google Drive/Gmail.
  3. Revoke permissions for anything you don’t actively recognize, trust, or use every week.

4. Run the Official Google Security Checkup

Lastly, visit myaccount.google.com/security-checkup. Google will walk you through:

  • Active devices logged into your account (remove old phones or unrecognized sessions).
  • Recent security events (password changes, unrecognized sign-in attempts).
  • Recovery phone numbers and backup email addresses (ensure an intruder hasn’t replaced your number with theirs).

The Takeaway: Trust, but Always Verify

We often assume that a strong password and two-factor authentication make us bulletproof. But technology platforms are full of subtle collaboration features that can become surveillance tools in the wrong hands.

Set a calendar reminder every six months to audit your Gmail settings. It takes under two minutes, and it guarantees that when you close your laptop, your inbox stays strictly between you and your recipients.

Have you ever audited your delegation settings before? Take a moment today to check—you might just be surprised by what you find.

How to Secure Your Data with Free Encrypted Cloud Storage

Are you looking for a secure and reliable way to store your files online? Do you want to access your data from anywhere, anytime, without compromising your privacy? If so, you might be interested in free encrypted cloud storage.

Continue reading How to Secure Your Data with Free Encrypted Cloud Storage

SAP HCM: Infotype Change Log

Have you been yourself in a situation where you think data was changed incorrectly but nobody knows what happed? Below are two key transactions on how to access Infotype change logs, for OM and PA infotypes. Note that they need to be previously configured.

For Personnel Management

  • IMG –> Personnel Management –>  Personnel Administration –> Tools –> Revision –> Set up change document
  • Tcode: S_AHR_61016380 – Logged Changes in Infotype Data


For Organization Management

  • IMG –> Personnel Management –>  Organizational Management –> Basic Settings –> Activate Change Documents
  • Program: RHCDOC_DISPLAY

¿Cómo extender tu wifi con los dispositivos TP-Link Deco M4?

Si vives en un edificio grande o tienes varias habitaciones en tu casa, es posible que tu wifi no llegue a todos los rincones. Esto puede ser un problema si necesitas conectarte a internet desde diferentes lugares, como el apartamento de tu madre o la habitación de tus hijos. Afortunadamente, hay una solución fácil y económica para extender tu wifi y disfrutar de una conexión rápida y estable en todo tu hogar: los dispositivos TP-Link Deco M4.

Los TP-Link Deco M4 son sistemas de wifi en malla que cubren una gran área con una señal wifi fuerte y estable . Estos dispositivos funcionan juntos para formar una red unificada con un solo nombre de red, y cambian automáticamente entre la mejor unidad Deco según te mueves por tu casa . Así, no tendrás que cambiar de red ni sufrir cortes o bajadas de velocidad.

Los TP-Link Deco M4 son muy fáciles de instalar y configurar. Solo necesitas descargar la aplicación Deco en tu teléfono móvil y seguir los pasos que te indica. La aplicación también te permite gestionar tu red, controlar el acceso de los dispositivos, crear perfiles de usuario, activar el control parental y mucho más .

Los TP-Link Deco M4 son compatibles con todos los proveedores de internet y routers. Además, son escalables, lo que significa que puedes añadir más unidades Deco si necesitas ampliar la cobertura. Cada unidad Deco M4 puede cubrir hasta 180 metros cuadrados, y un paquete de tres unidades puede cubrir hasta 550 metros cuadrados . También puedes conectar dispositivos por cable a los puertos Ethernet que tiene cada unidad Deco M4.

Los TP-Link Deco M4 son una opción ideal para mejorar tu wifi y tener una conexión de calidad en todo tu hogar. Con estos dispositivos, podrás navegar por internet, ver vídeos, jugar en línea y hacer video llamadas sin problemas. Si te interesa comprar los dispositivos TP-Link Deco M4, puedes encontrarlos en diferentes tiendas online o físicas. Por ejemplo, puedes visitar el siguiente enlace:

Tp-link M4 Deco: Sistema Wi-Fi Mesh Inteligente de Doble Banda AC1200. Aquí puedes encontrar más información sobre las características y especificaciones de los dispositivos, así como los distribuidores autorizados en España.

Why are there no older SAP consultants working?

SAP is a business management software that is used by many companies around the world. To implement and use this software, companies need SAP consultants, who are professionals who offer services for the adaptation, optimization and execution of SAP products1. SAP consultants are in high demand and well paid in the labor market, but they also face many challenges and demands.

One of the issues that can be observed is the shortage of older SAP consultants working. This may have several reasons, but some of the possible ones are:

  • The constant evolution of SAP software. SAP software is always updating and incorporating new features and technologies, such as SAP S/4HANA2, which is the latest version of the software. This means that SAP consultants need to be constantly recycling and certifying themselves in the new versions and modules of the software. This can be difficult and tiring for older consultants, who may have difficulties to keep up with the changes and adapt to the new tools.
  • The high competitiveness of the market. As SAP consultants are highly sought after, they also face a lot of competition among themselves. Younger consultants may have advantages over older ones, such as greater availability, flexibility, dynamism and knowledge of new trends. In addition, customers may prefer to hire younger consultants, because they believe they have more capacity for innovation and problem solving.
  • The lack of career opportunities. Many SAP consultants work as freelancers or by projects, which can generate instability and uncertainty about their professional future. Older consultants may miss opportunities for growth and recognition within companies or in the market. They may also have difficulties to find new projects or clients, especially if they do not have a good network of contacts or a good reputation.
  • The demotivation and professional burnout. SAP consulting is an activity that demands a lot from professionals, both in technical and emotional terms. SAP consultants have to deal with tight deadlines, pressure from clients, constant travel, frequent changes of environment and team, interpersonal conflicts, etc. This can generate a high level of stress and dissatisfaction at work, which can affect the physical and mental health of consultants. Older consultants may feel more the negative effects of this situation and lose interest or passion for their work.

These are some of the possible explanations for the low presence of older SAP consultants working. However, this does not mean that older consultants do not have value or potential to work in this area. On the contrary, they may have a lot of experience, knowledge and skills that can be useful and differential for projects and clients. In addition, they can benefit from some strategies to improve their professional situation, such as:

  • Seek constant updating. SAP consultants should always be attentive to the novelties of the software and the market and seek to train themselves in the new versions and modules of SAP. They should also expand their knowledge in other areas related to business management, such as finance, logistics, marketing, etc.
  • Build a good network of contacts. SAP consultants should maintain a good relationship with their colleagues, clients, partners and suppliers, as this can generate work opportunities and referrals. They should also participate in events, forums, communities and social networks focused on SAP consulting, as this can increase their visibility and credibility in the market.
  • Seek new challenges and opportunities. SAP consultants should be open to new experiences and possibilities of work, such as changing area, company, country, etc. They should also look for projects that are compatible with their interests, goals and values, and that provide them with learning, satisfaction and recognition.
  • Take care of health and well-being. SAP consultants should have a balanced routine that includes healthy habits of eating, sleeping, exercising and leisure. They should also seek professional or personal support when they feel they are suffering from stress, anxiety, depression or other emotional problems.

In conclusion, older SAP consultants may face some difficulties to remain active and competitive in the labor market, but this does not mean that they cannot continue to perform their profession with quality and success. They should value their strengths, seek their updating and motivation and take care of their health and well-being.